

 Contact Us




THE ARGUMENT
An alert is just the start of an investigation
Alerts alone leave analysts investigating and AI agents unable to act.
RevealX NDR automatically assembles evidence into a case—including identities, protocols, sequences, and timing—with confidence scores and blast radius details to drive effective action.
What an alert provides
— A signal fired
— A source and a destination address
— A severity number
— A link telling you to go look somewhere else
What RevealX provides
- What happened, and how confident we are
- Which assets, and which identities
- The sequence and timing across the kill chain
- Blast radius, already scoped
- The decrypted transactions behind the finding
- The packets, one click down
THE AGENTIC ERA PLATFORM
Give AI agents the context to act fast
An agent working from partial data makes misguided decisions with confidence and takes incorrect action at machine speed. Agents' reasoning on complete, pre-correlated context drives MTTA (mean time to acknowledge) toward zero, compressing detection and containment.

Accurate
Attackers can disable endpoint agents and wipe logs, but every attacker must communicate to move or steal. RevealX reads the communication on the wire as it happens.

Defensible
Every conclusion traces to the transaction and the packets underneath, through one API and one audit trail. Auditors, regulators, and boards see the proof already attached to the decision.

Affordable
Agents start at the highest-signal tier that answers the question, descending only when a hypothesis requires more depth, keeping token and compute costs predictable.

5 Context Tiers
WHAT IT HOLDS
RevealX scores and prioritizes every finding. Machine learning and rule-based detections assemble into cases with blast radius attached.
THE QUESTION IT ANSWERS
Is this real, how bad is it, and what did it touch?
Context
See the whole attack surface
RevealX NDR covers the whole attack surface, data centers, cloud, containers, Kubernetes, remote, edge, and OT, and every device, workload, and identity in real time, with AI observability across agents, LLMs, and MCP servers.
Across multi-cloud and hybrid environments, without deploying agents everywhere.
WHAT IT IS
RevealX builds a continuous, run-time inventory of everything communicating on your network.
HOW EXTRAHOP DOES IT
RevealX discovers and profiles every device, server, service, and identity from the wire, with no agent to install. Each entity carries more than 5,000 metrics. Device groups map assets to business function, so criticality and data sensitivity travel with the context.
WHY IT IS DIFFERENT
A CMDB records what someone said was there. RevealX discovers IoT, OT, unmanaged, contractor, and ephemeral workloads that never receive an agent. RevealX also sees any host where an attacker disabled the agent. Network traffic reveals every one of them, and an attacker cannot uninstall the network.
DETECTION
Four detection methods. One case structure.
Different attacks give themselves away in different ways. RevealX runs four methods against the same decoded traffic, landing every finding into one case structure.

Cloud-scale machine learning
Models retrain continuously and update live. Central analysis spans every sensor, so a model sharpened in one environment sharpens detection everywhere. On-premises detectors run without a dedicated appliance.

Rule-based and behavioral patterns
Rule-based NDR and IDS analytics run against decoded traffic in real time. The rules match behavioral patterns rather than file hashes. A small change defeats a hash. Behavior stays much harder to disguise.

Threat intelligence matching
RevealX cross-references network context against threat indicators in real time. Indicators come from ExtraHop Reveal Labs and from partners, including CrowdStrike, through Collective Threat Analysis.

Retrospective detection
RevealX rechecks stored traffic automatically whenever a new indicator arrives. A detection can surface today for activity that passed unnoticed last month. Your team answers, “Are we affected?” with a query.
INVESTIGATION
From alert to evidence
Analysts spend most of an investigation assembling data. Alert details sit in one tool, the identity in a second, asset data in a third, the transaction in a fourth, and the packet in a fifth. RevealX NDR automatically assembles all five context types into one case.
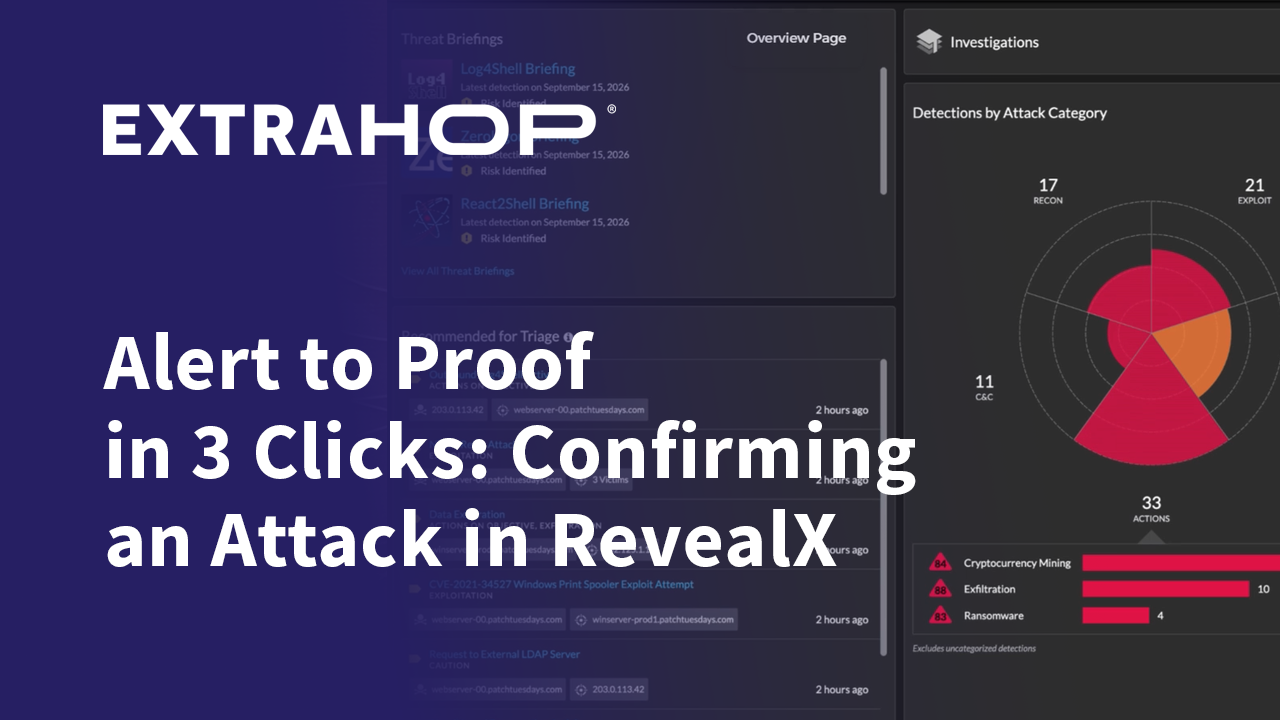

Alert to Proof in 3 Clicks: Confirming an Attack in RevealX

RESPONSE
Act where your team already works
RevealX NDR drives action inside the tools your team already runs.

Recommended mitigation
Every case carries the blast radius and recommended action, as well as MITRE ATT&CK mappings for severity and next steps.
Automated or push-button response
Triggers workflows your stack already runs: enrich a ticket, direct EDR containment, or push scoped blast radius to SIEM or SOAR.
API and MCP
The REST API and the MCP server expose every finding through one authentication and one audit trail. Analysts, scripts, and AI agents query the same structure.

Intrusion Detection System
Integrated IDS combines high-fidelity signatures with cloud-scale behavioral threat analysis to reduce MTTR and secure the entire attack surface.
Unified sensor detections
Consolidates curated IDS detections into the ExtraHop RevealX NDR platform on a single sensor, replacing fragmented tools to block both known exploits and zero-day attacks.
Comprehensive threat coverage
Covers over 40 emerging threat categories, including malware delivery, C2, credential phishing, DDoS, botnets, and SCADA exploit kits across all network traffic.
Consolidated full-surface defense
Retires costly legacy IDS appliances and runs NDR, NPM, packet forensics, and intrusion detection on a single platform, multi-function sensor.
Complete detection transparency
Provides full visibility into the curated IDS ruleset using an in-platform detection catalog to verify coverage for specific CVEs and satisfy audit requirements.

Packet Forensics
Continuous hybrid cloud PCAP gives engineers and AI agents immediate, unalterable telemetry for fast triage and root-cause analysis.
Complete visibility
Enables analysts to view, filter, and dissect TCP/UDP/HTTP streams inside the RevealX platform using familiar Wireshark-like controls.
Line-rate telemetry
Captures and indexes full L2-L7 packets at line rate without latency and uncovers hidden threat activity in encrypted traffic without relying on risky man-in-the-middle architectures.
Defensible context
Attaches auditable telemetry to transaction records providing engineers and AI workflows with zero-impact access for rapid investigation.
Scalable PCAP repository
Scales forensic lookback repositories up to petabytes of storage across multi-cloud, on-premises, and remote/IoT deployments to fulfill chain-of-custody and compliance mandates requiring packet capture.
DATASHEET
Speed Your Forensic Investigations and Evidence Collection with Packet-Level Visibility
Recognition
Independently graded
“Right out of the box, we plugged RevealX into the network and turned it on at 8:00, and it was scanning our network by 8:01. As the day went on, we continued to get alerts—but none of our other security tools indicated that we had an issue. After a simulation of the domain takeover at 8:00 that night, we finally got an alert from another tool indicating that an incident had taken place—far too late to act on the information.”
Todd Williams
Director of Information Security
155%
Return on Investment
63%
Faster Investigations


Compare
Where other approaches lose visibility
Most teams depend on approaches that leave blind spots.
The stack an attacker can switch off.
WHERE VISIBILITY STOPS
An attacker with root disables the endpoint agent and clears the logs, a common step in advanced cyberattacks.
WHAT IT COSTS YOU
Your record of the intrusion ends exactly where the intrusion gets serious.
HOW REVEALX SEES ALL
Out-of-band sensors keep recording through the compromise. There is nothing on the host for an attacker to switch off.
Associated Content
See how RevealX NDR can transform your security operations



Start with context you can trust
Accuracy begins at collection. RevealX NDR collects everything on the wire, so detection and investigation deliver trustworthy results.