

 Contact Us



HOW REVEALX WORKS
From Network Traffic to Decisive Action in Real Time
Ingest and analyze massive enterprise traffic in real time to optimize performance and stop threats before impact.
Gartner® named ExtraHop a leader in network detection and response two years in a row.
Overview
How RevealX works
Every connected system, managed or unmanaged, must transmit data across the wire to operate. By decoding protocols, ExtraHop delivers the deep analysis needed to uncover threats hiding in encrypted traffic, respond to cyber risk, and ensure uninterrupted business operations.
INGEST
Monitor traffic across hybrid and multi-cloud networks
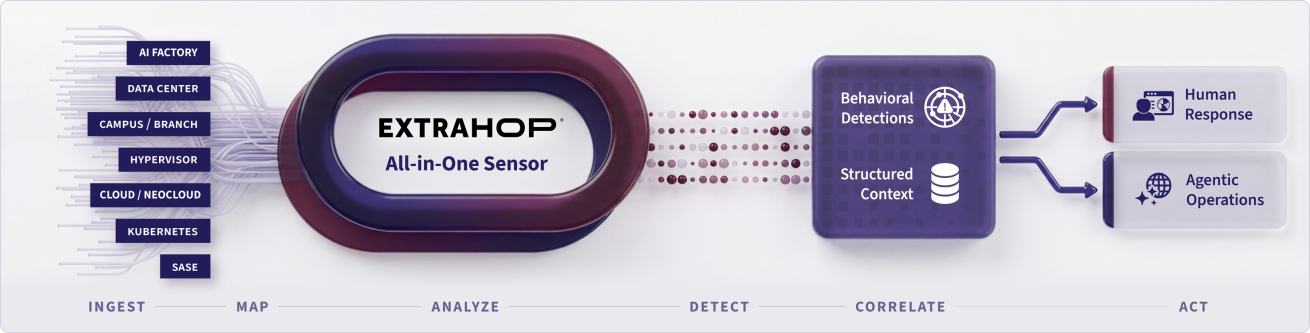
ExtraHop passively ingests a copy of network traffic across on-premises, cloud, and virtual environments. By analyzing full-volume traffic without sitting inline, ExtraHop delivers continuous visibility without slowing down or disrupting the business.

See more without disruption
Gain visibility without installing endpoint agents or placing appliances inline.

Deploy wherever you need visibility
Gain visibility across AI factories, datacenters, cloud, virtual, and hybrid environments. Physical and virtual sensors meet traffic where it lives, helping security and IT teams maintain a unified view as infrastructure evolves.

Analyze traffic at enterprise scale
Analyze high-volume traffic at up to 400 Gbps without sampling. Greater capacity means fewer sensors to deploy and manage, and more complete evidence for faster response and reduced operational overhead.
What is the best data source for security AI agents?

MAP
Continuous asset discovery and dynamic dependency mapping
You can't defend or optimize what you can't see.
ExtraHop continuously auto-discovers and classifies every managed, unmanaged, cloud-native, and AI asset across your hybrid environment, including AI agents, LLMs, and MCP servers. The live inventory and dependency map build from network traffic, without endpoint agents or manual inventory.

Wire truth for every analyst and every agent
Feed an AI agent stale CMDB data and it will act on the wrong answer at machine speed. ExtraHop delivers continuous, wire-derived context that reflects your environment as it actually is, so analysts and AI workflows act on evidence, not assumptions.

Understand criticality and blast radius
Automatically categorize assets by business role to track high-risk users, executive identities, and critical infrastructure with heightened vigilance. Map real-time application dependencies to pinpoint the blast radius of incidents and analyze the root cause.

Eliminate blind spots
Instantly surface rogue cloud workloads, IoT/OT hardware, and unmanaged employee and third-party devices where endpoint AI agent installation is impossible.
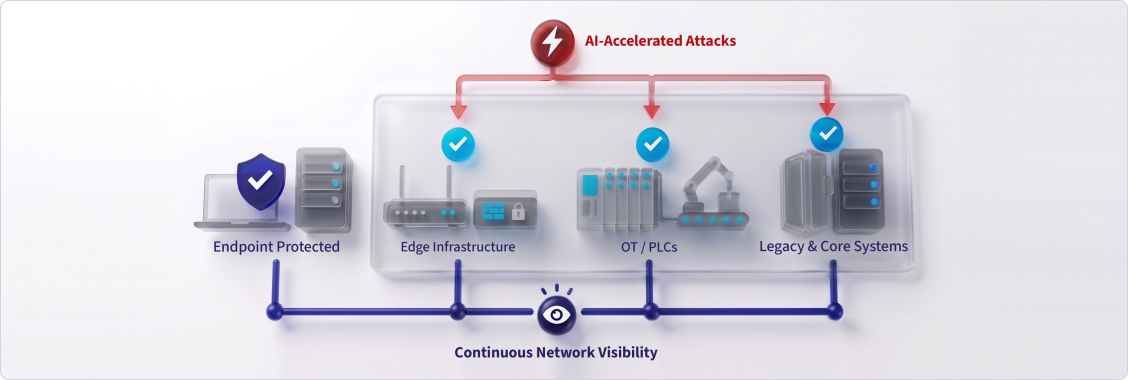
AI-accelerated attacks increasingly target critical infrastructure beyond the reach of traditional endpoint tools. ExtraHop continuously discovers and monitors edge devices, OT systems, and legacy platforms through network traffic, without requiring agents.
ANALYZE
Behavioral detection and deep protocol intelligence
Most tools only look at OSI Layers 2 through 4, telling you what connected to what. ExtraHop decodes Layers 2 through 7 to reveal who connected to whom and what they actually did.
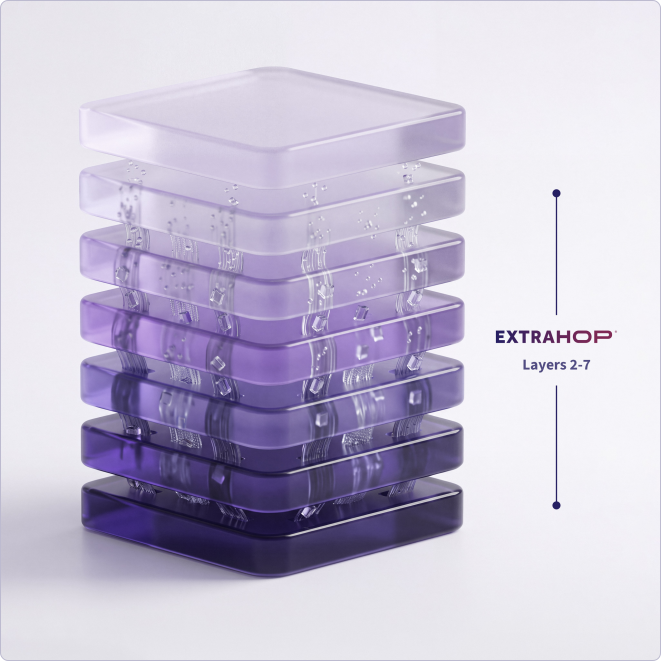

Uncover encrypted threats
Safely decrypt TLS 1.3 traffic in real time to inspect API calls, database queries, and authentication requests to expose threats hiding in encrypted streams and pinpoint microsecond slowdowns.

Hunt threats without decryption
Leverage native JA4+ fingerprinting to profile encrypted traffic patterns, exposing modern C2 frameworks, malware, and rogue applications even when decryption isn't permitted due to privacy compliance.

Learn normal, spot abnormal
ExtraHop automatically learns how every user, device, and application normally behaves, and continuously updates this baseline to instantly flag anomalies, from unseen threats to IT slowdowns.
Detect
Prioritized threat, exposure, and performance alerts
ExtraHop turns raw network anomalies into prioritized, actionable detections. By mapping network behaviors against the MITRE ATT&CK framework and real-time operational baselines, ExtraHop filters out benign background noise so your team focuses on critical risks.
ExtraHop exposes issues across three core pillars:

Active threats and attack tactics
Detect stealthy intruder behavior such as lateral movement, credential abuse, privilege escalation, and suspicious remote monitoring and management (RMM) tools before data loss occurs.


Proactive exposure and hygiene
Surface hidden vulnerabilities across your footprint, from weak cipher suites and expiring certificates to shadow AI, unauthorized AI agents, and sensitive data sent to external LLMs.

Operational and service failures
Automatically flag database timeouts, DNS degradation, application errors, and network saturation caused by resource-hogging devices before end users suffer downtime.
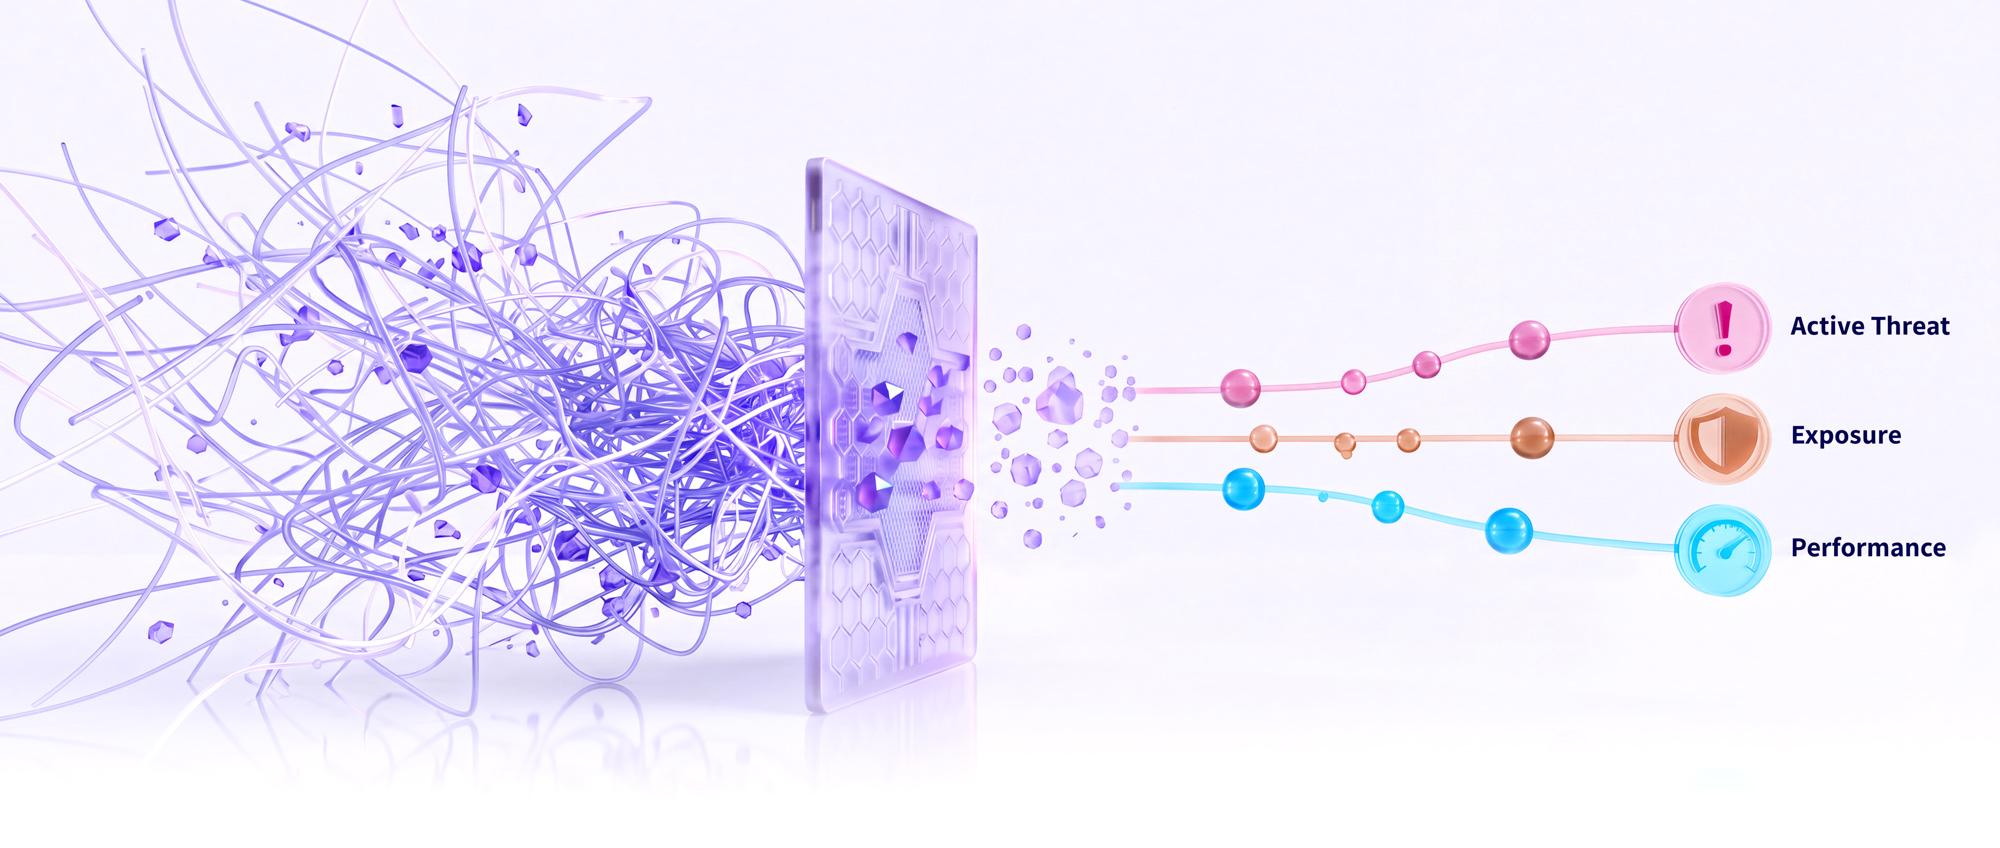
Inline analysis sits directly in the traffic path, so inspection can add latency, especially under heavy load. ExtraHop analyzes mirrored traffic out of band, avoiding latency and keeping the analyzer out of the critical path.
CORRELATE
Full-spectrum context without silos
ExtraHop connects the dots across your entire stack. By uniting network wire data with endpoint telemetry, identity context, and cloud logs, ExtraHop transforms scattered alerts into unified incident timelines, enriching your SOC and NOC tooling with ground truth.
ACT
Fuel human and autonomous response
Response tools are only as smart as the context they receive. ExtraHop supplies the ground truth for your security stack, feeding rich network context to your SIEM, SOAR, and AI agents so they act precisely and resolve incidents quickly.

Execute response with certainty
Packet-level evidence means an analyst isn't guessing before they block a connection, isolate a host, or kill a session. Backed by definitive proof rather than a guess, analysts act with confidence.

Ensure agents respond accurately
Autonomous agents cannot operate effectively on raw, disconnected telemetry. ExtraHop provides pre-built, structured context that is already enriched, correlated, and ready for machine reasoning.

Verify the fix worked
ExtraHop keeps watching after a response action to confirm the threat actually stopped with no reinfection, no lateral movement resuming.
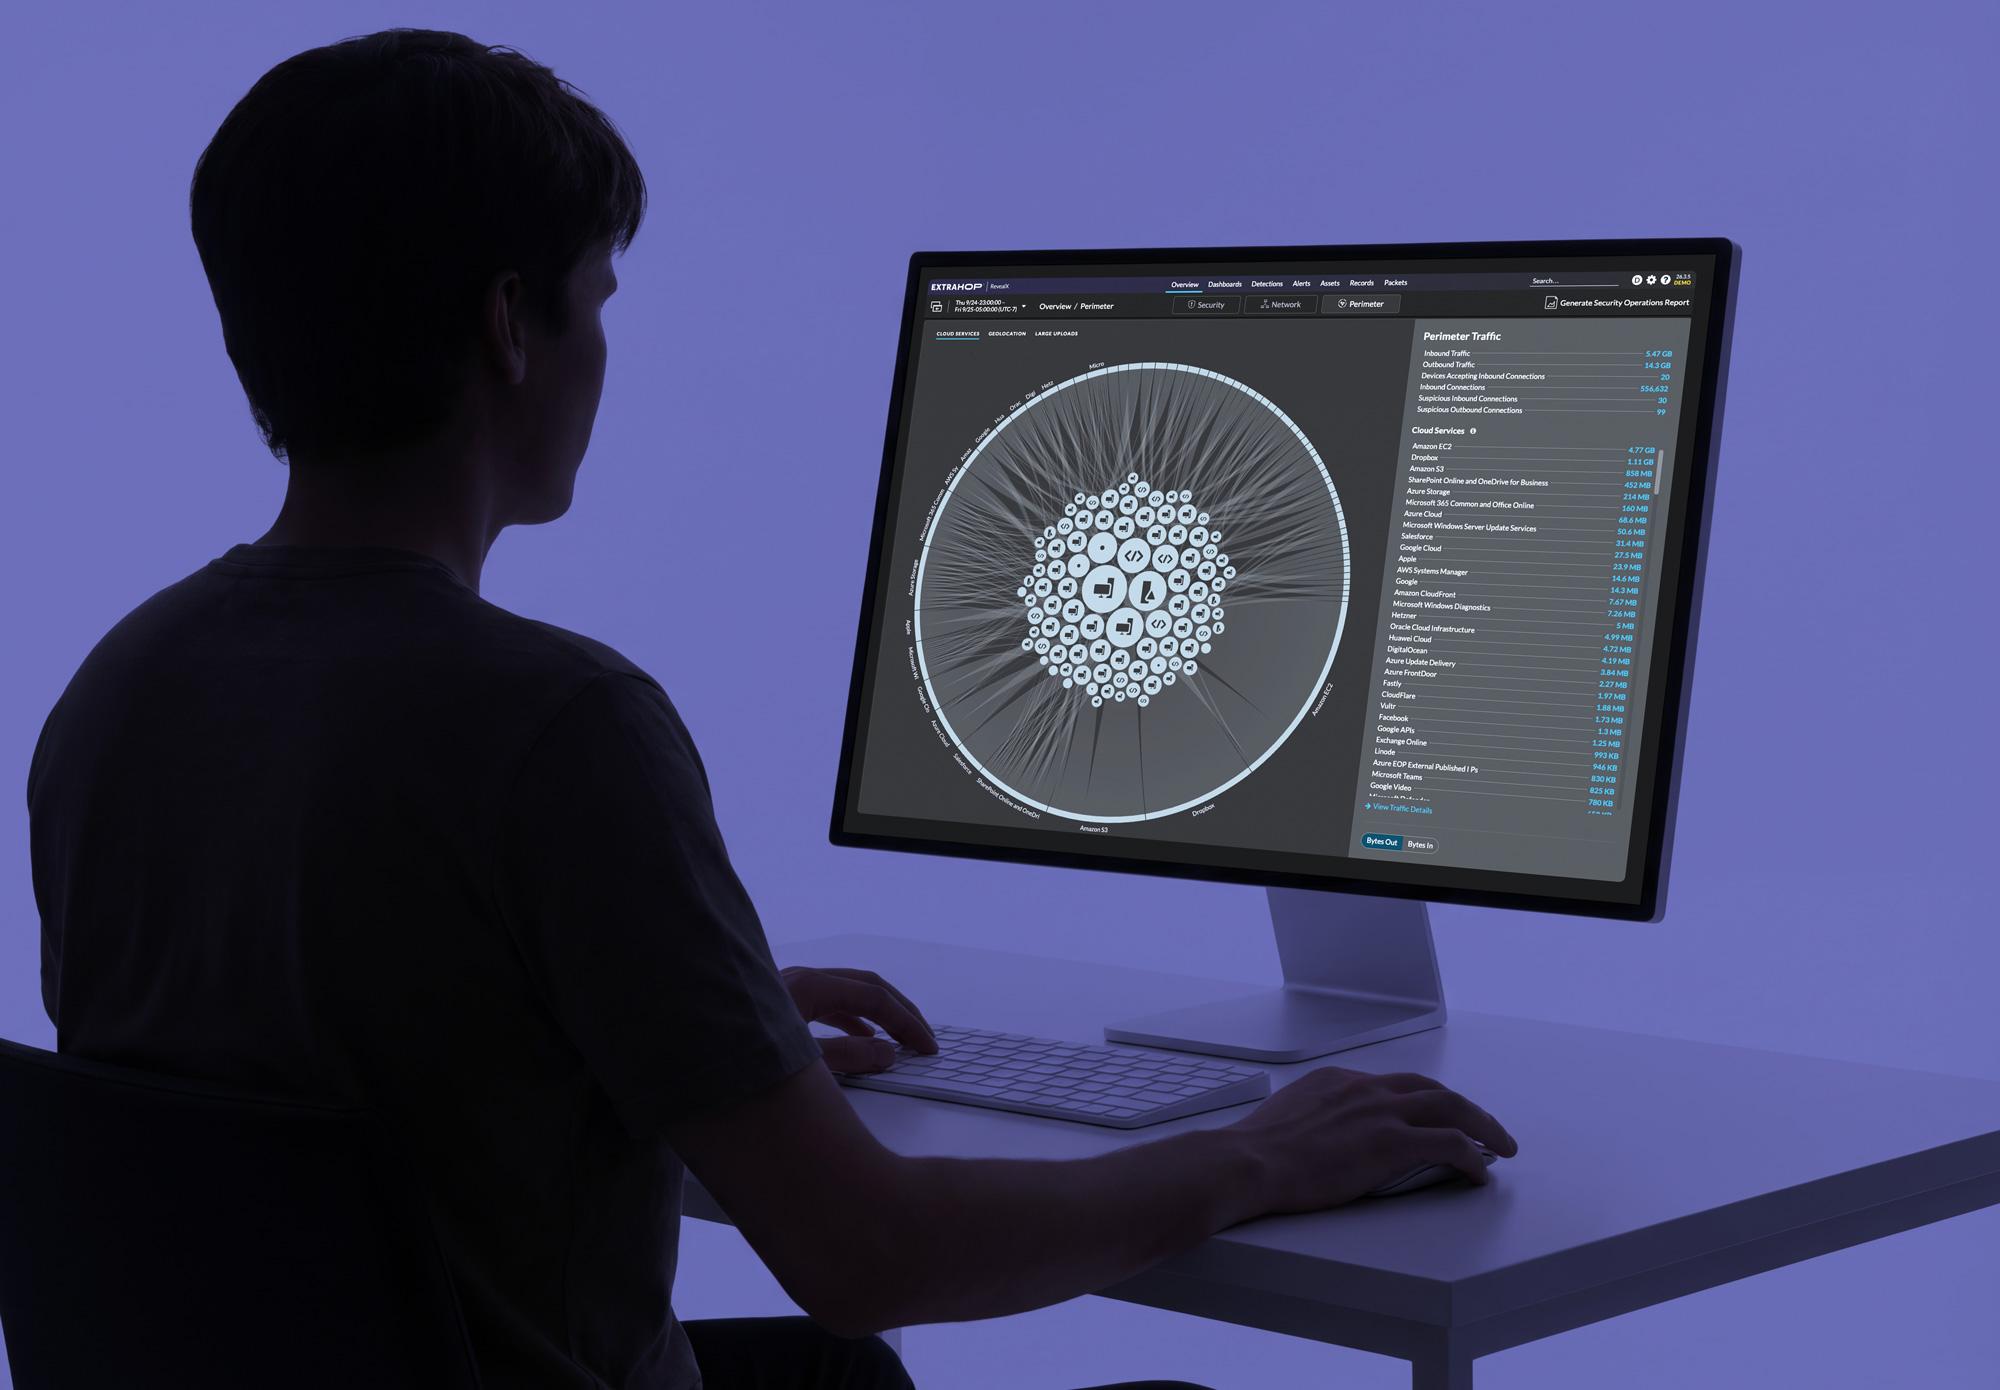
ExtraHop RevealX platform
Ingest and analyze massive enterprise traffic in real time to optimize performance and stop threats before impact.
Start with context you can trust
Accuracy begins at with visibility. RevealX NDR observes and analyzes everything on the wire, so detection and investigation deliver trustworthy results.
Associated Content