ExtraHop® Closes Enterprise Data Center Blind Spots with new 400 Gbps sensor

Search
  • Solutionschevron right
  • Industrieschevron right
  • Platformchevron right
  • Resourceschevron right
  • Customerschevron right
  • Companychevron right

DETECTION OVERVIEW

New WSMan Request Activity

Risk Factors

Web Services-Management (WSMan) tools such as PowerShell remoting are normally only available to local administrators. An attacker with administrator credentials can take advantage of WSMan tools to gain remote access to a server. The amount of potential damage depends on the privileges available on the compromised server.

Category

Lateral Movement

Decryptions

TLS Decryption
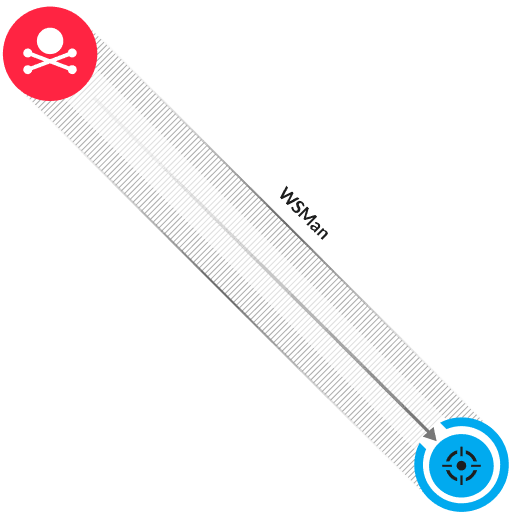
Detection diagram
Next in Lateral Movement: New Windows Registry Modification Attempt

Background

WSMan is an open-source, SOAP-based protocol that transports a command from a client to a tool on a remote server that will run the command. The command is wrapped in XML schemas and encrypted with a session key negotiated through the Kerberos protocol. The command is then transported over HTTP or HTTPS to the tool, which is a local implementation of WSMan. For example, the tool can be PowerShell Remoting Protocol (PSRP) or WinRM, which is the Microsoft implementation of WSMan.

An attacker who steals administrator credentials can leverage WSMan tools to run malicious commands on a remote device without installing any files. An attacker sends a WSMan request that is authenticated with a client principal name (CPN). The request contains a malicious command, which is then run by the victim. The attacker can now gain access to the victim and move laterally to new targets.

Mitigation Options

Disable PowerShell Remoting on devices where remote access is unnecessary

Complete all remote administration tasks from a dedicated management host

Create a group policy object (GPO) to only allow remote administration from trusted groups

Disable NTLM authentication, which is less secure than Kerberos

Disable HTTP handler and route traffic securely through HTTPS

MITRE ATT&CK ID

Associated content

Announcing The Forrester Wave™: Network Analysis And Visibility Solutions, Q4 2025

Network analysis and visibility solutions remain underrepresented in enterprises. Find out why in this preview of a new Wave report.

Report

ExtraHop® Named a Leader in First-Ever Gartner® Magic Quadrant™ for Network Detection and Response — ExtraHop

ExtraHop® Named a Leader in First-Ever Gartner® Magic Quadrant™ for Network Detection and Response

News

Detections

Visit this resource for more information.

Documentation

Decryption

Learn how ExtraHop decryption works.

Documentation

The 2025 ExtraHop Global Threat Landscape Report: The Alarming Reality of Threat Actor Dwell Time and Deeper Network Access — ExtraHop

This analysis exposes the critical link between an organization's lack of internal visibility and the escalating cost of compromise, demanding an urgent re-evaluation of how core business assets are protected.

Blog Post

ExtraHop RevealX MITRE ATT&CK Coverage 2024 — ExtraHop

Learn why you need to be wary of the claims certain network detection and response providers make about their coverage against the MITRE ATT&CK framework.

Blog Post

MITRE ATT&CK - Network Detection & Response with RevealX — ExtraHop

Learn how NDR from RevealX helps security teams detect and investigate more adversary TTPs in the MITRE ATT&CK framework than rule-based tools.

External
Periodic Table of Use Cases

What else can RevealX do for you?